Security & data flow
This page gives IT and security teams a high-level overview of where data goes when you use VIKTOR, how it is protected, and who can access it. For certifications and policies, visit our Trust Center.
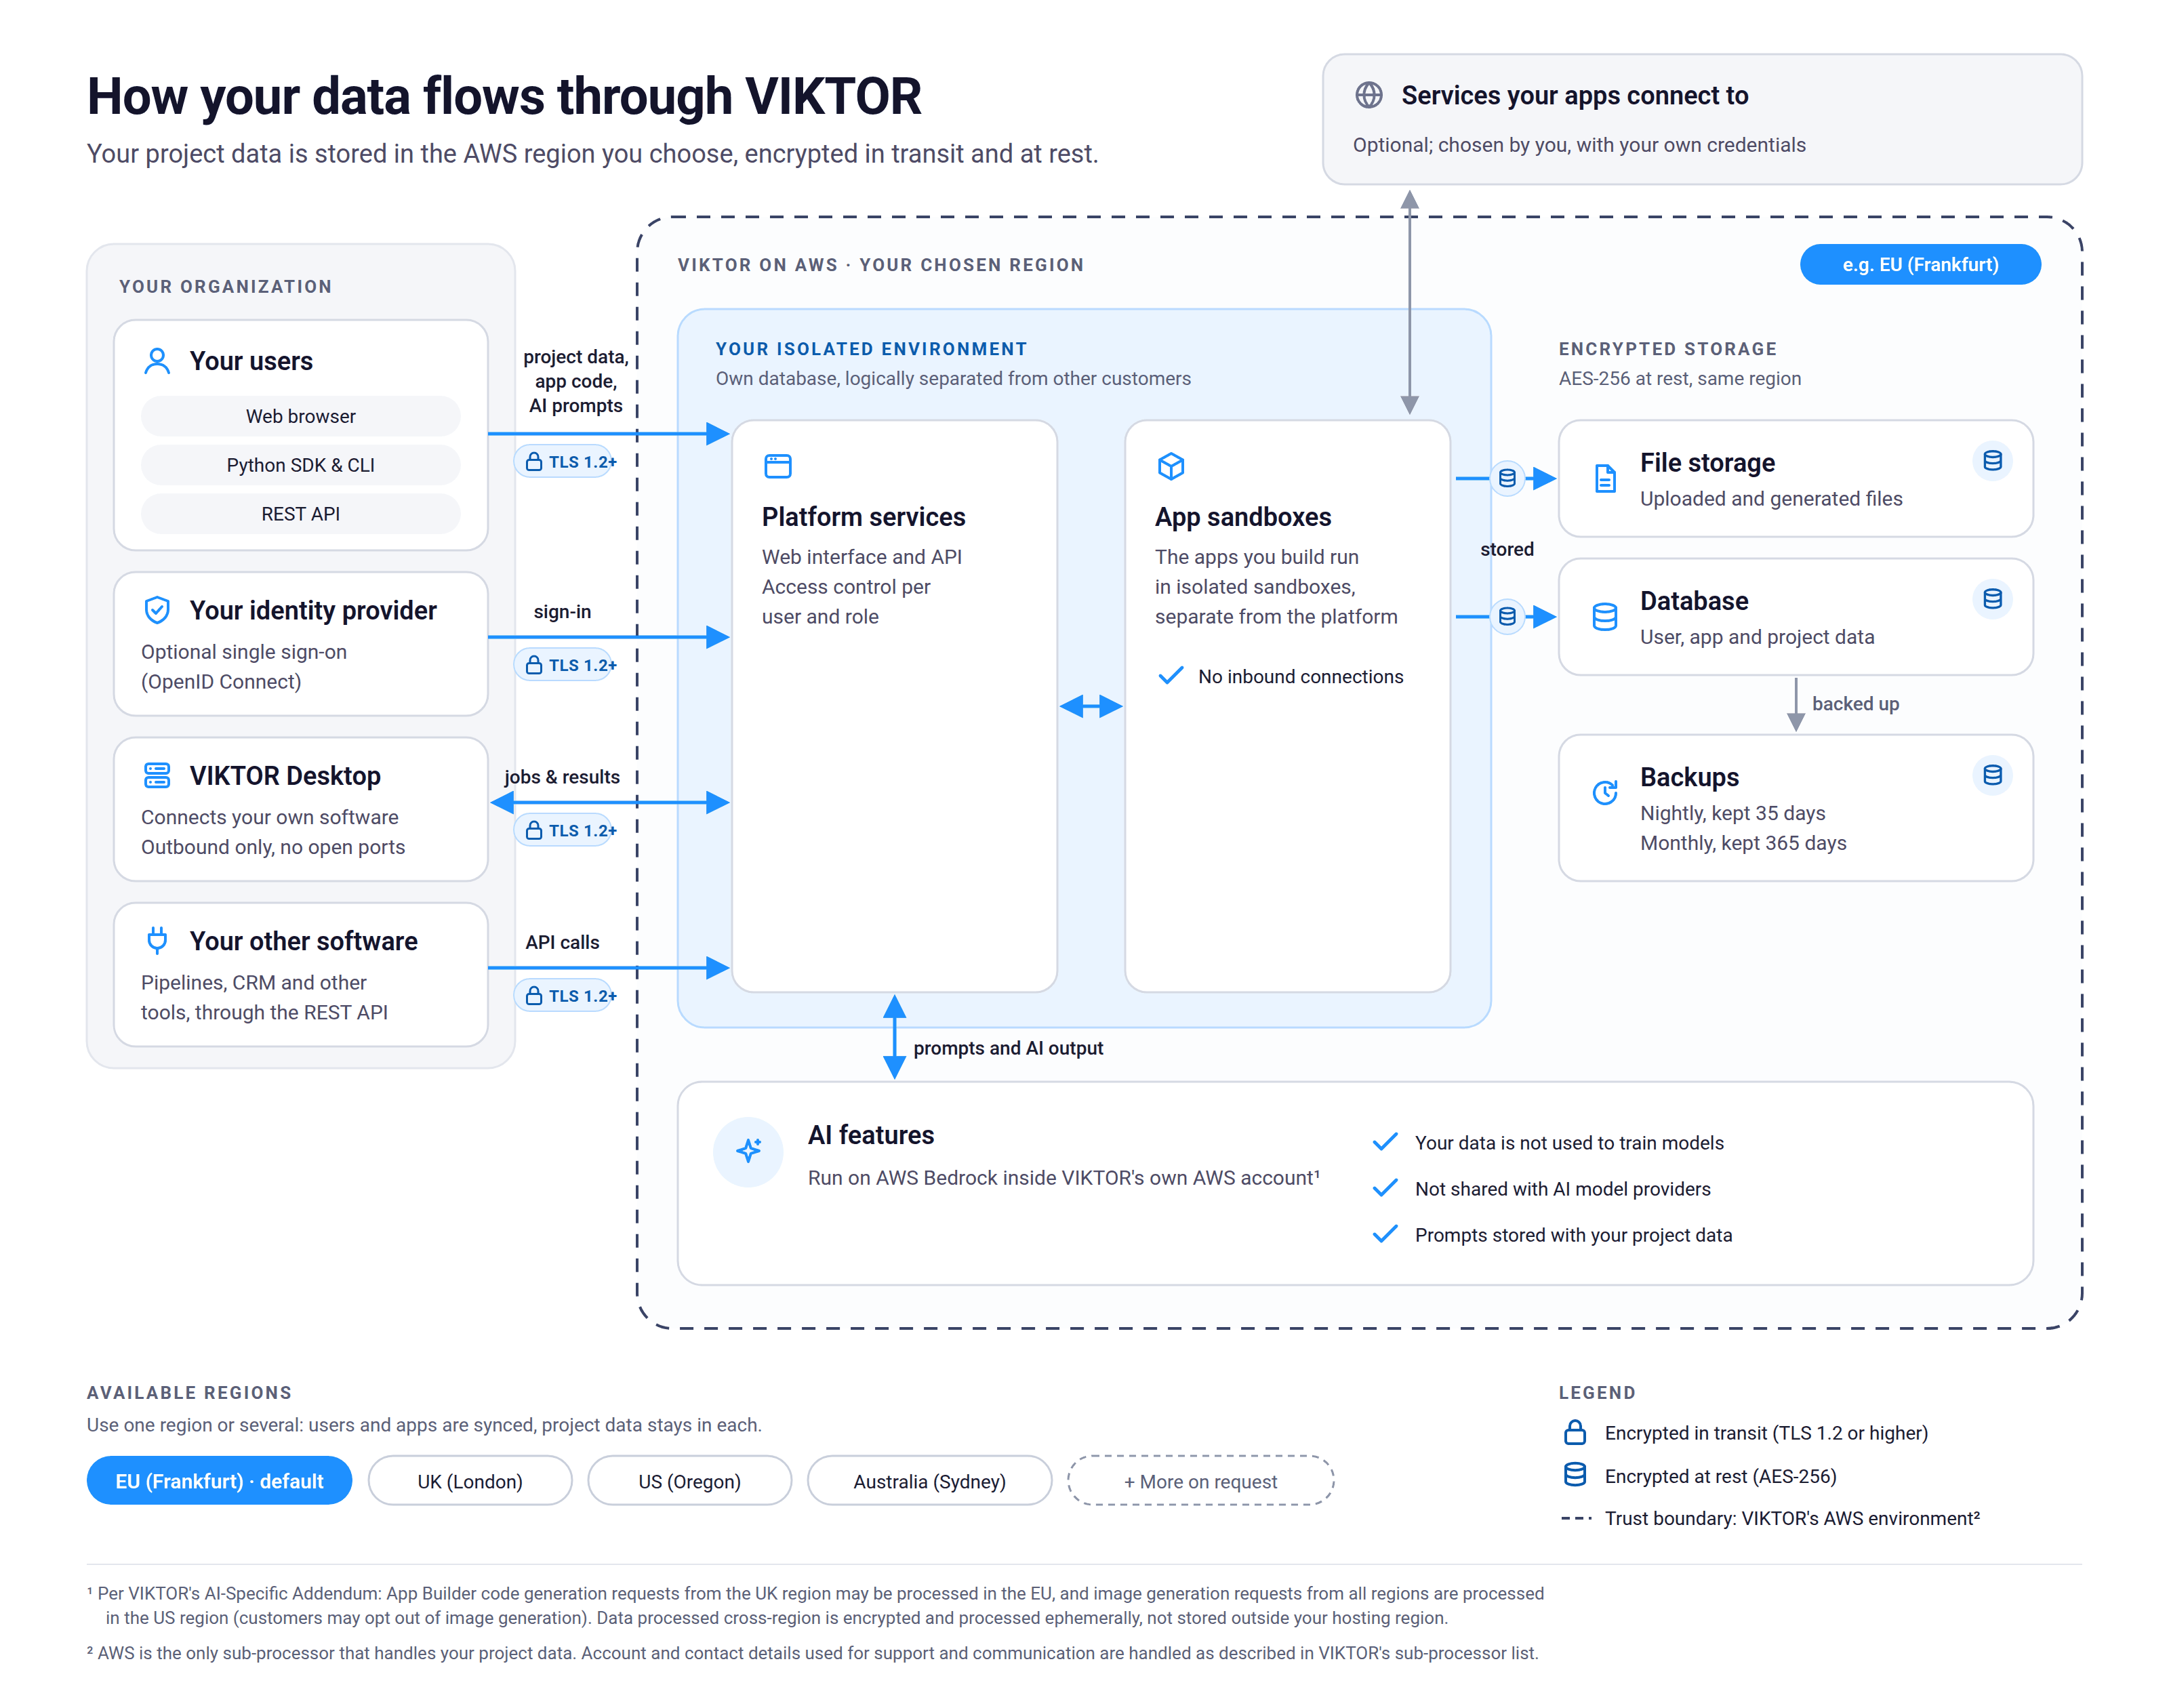 How your data flows through VIKTOR
Connecting to VIKTOR
- All connections between your organization and VIKTOR are encrypted using TLS 1.2 or higher. This applies to the web browser, the Python SDK and CLI, and the REST API. Your other software, such as pipelines or a CRM, can connect through the REST API in the same way.
- Users can sign in through your own identity provider using single sign-on (OpenID Connect).
- VIKTOR Desktop connects your apps to software installed on your own machines. The connection is always made outbound from your machine over port 443, so no ports need to be opened to the internet. See Integrations for details.
- The network requirements for developers are listed on the Enterprise IT page.
Your environment
- Each customer environment has its own database and is logically separated from other customers.
- The apps you build run in isolated sandboxes, separate from the platform services. Sandboxes accept no inbound connections from the internet.
- Access within your environment is controlled per user and role. See User & access management.
Data storage and backups
- Your data is stored in the region you choose: EU (Frankfurt, default), United Kingdom (London), United States (Oregon) or Australia (Sydney). Additional regions are considered on request. When you use several regions, users and apps are synced between them, while app data stays in the region where it was created.
- Databases, file storage and backups are encrypted at rest using AES-256.
- The database is backed up nightly and monthly. Nightly backups are kept for 35 days and monthly backups for 365 days, in the same region as your data.
- The recovery point objective (RPO) is 8 office hours.
AI features
AI features run on AWS Bedrock inside VIKTOR's own AWS account. Your data is not used to train AI models and is not shared with AI model providers. The model processes requests ephemerally and does not keep your data. Your prompts and the AI output are stored with your project data in your region, under the same retention and deletion terms.
Some AI requests may be processed outside your hosting region: App Builder code generation requests from the United Kingdom region may be processed in the EU, and image generation requests from all regions are processed in the United States region. Customers can opt out of image generation. See the AI-Specific Addendum for details.
Audit log
The Activity dashboard records platform events such as sign-ins, failed sign-ins, account lockouts, invitations, removed users, published apps and the use of AI features. You can export the log as CSV.
Services your apps connect to
Apps can connect to external services that you choose, for example through OAuth 2.0 integrations or API tokens, or by using your own API keys for an LLM provider. The data sent to those services is determined by your app, and is governed by your own agreements with those providers.
Sub-processors
Within VIKTOR, AWS is the only sub-processor that handles your project data. Account and contact details used for support and communication are handled as described in our sub-processor list.